Ohio State regularly runs phishing training exercises to the university community. By clicking the link that brought you to this page, you succumbed to a university phishing simulation. Read on to learn how to spot phishing messages and protect yourself and the university from malicious attacks.
Spotting the Phish
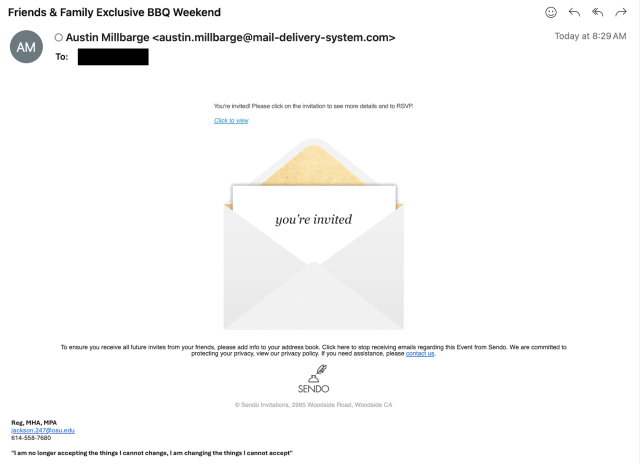
You received this email:
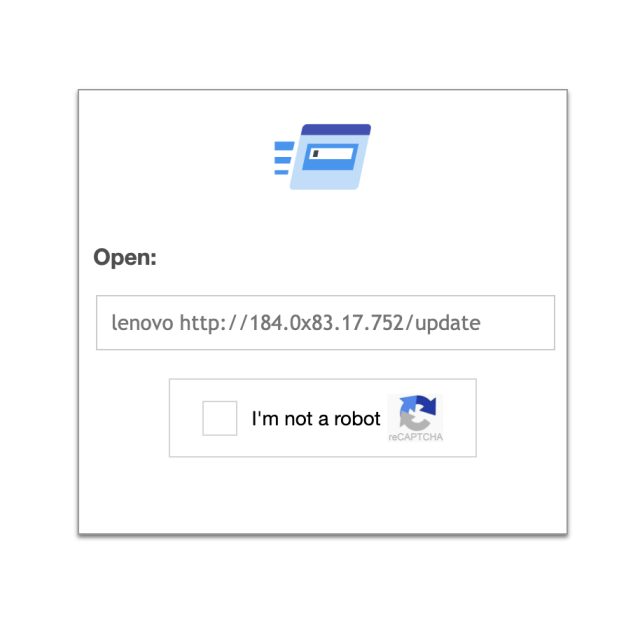
When you click from this email, you are taken to a generic login page:
Sender Addresses: The sender address, austin.millbarge@mail-delivery-system.com, is not known to you. In fact, that is Dan Aykroyd's character from the 1985 comedy "Spies Like Us". If you look closely, the domain is mail-delivery-system.com is generic and suspicious. You should remain skeptical of addresses that some from outside Ohio State. The domain (everything after the @ symbol) is the first indication that this might be a phishing attack.
Review the URL of web page before engaging with it: When you clicked from the email, a website was loaded with a URL of https://invite.mail-delivery-system.com which is not a legitimate site. Attempt to confirm the legitimacy of a site before you enter login credentials or personal information like name, email address or phone number.
Report Phishing Attempts
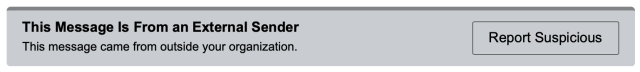
If you ever suspect an email to be a phishing attempt, please report it immediately by clicking the "Report Suspicious" button in the warning banner which appears at the top of that external email.